The safest crypto wallets combine strong private-key protection, secure transaction verification, reliable recovery options, transparent firmware and independent security testing. No single wallet is universally safest because hardware isolation, transaction security and recovery resilience protect against different threats.
In this guide, The Coin Bureau independently scores each crypto wallet using a proprietary 100-point security framework rather than relying on chip certifications or air-gapped designs alone. Private-key protection, transaction signing, firmware integrity, recovery resilience, security history and independent testing are evaluated separately.
Editor's Note (Nov. 4, 2026): We fully updated this guide in November 2026 to introduce The Coin Bureau's proprietary 100-point Wallet Security Score and provide a more rigorous, evidence-based ranking of the safest crypto wallets. This refresh reassesses the leading hardware, software, air-gapped, and seedless wallets, updates our recommendations, and incorporates recent security vulnerabilities, independent audits, and firmware disclosures. We also expanded our analysis of private-key protection, transaction verification, recovery resilience, and real-world security risks, while adding clearer comparisons and practical guidance to help readers choose and use a secure crypto wallet.
Most Secure Crypto Wallets in 2026: Quick Verdict
Trezor Safe 7 is our safest overall crypto wallet, followed closely by Ledger Flex for everyday multi-asset use. BitBox02 Bitcoin-Only Edition leads for Bitcoin savings, OneKey Pro 2 offers premium hardware signing, and Rabby stands out for DeFi security. SafePal S1 and ELLIPAL Titan 2.0 provide QR-based signing, while Zengo offers seedless MPC recovery.
Crypto holders who want strong private-key protection, reliable transaction verification and tested recovery options. Hardware wallets are particularly suitable for long-term savings, while transaction-aware software can help active DeFi users identify risky approvals.
Users who cannot securely protect recovery credentials, verify transaction details or maintain wallet updates. Even highly ranked wallets cannot prevent losses from exposed backups, malicious approvals or incorrectly configured recovery methods.
| Wallet | Best For | Security Score | Wallet Type | Key Protection | Signing Protection | Recovery Method | Independent Evidence | Major Disclosed Risk |
|---|---|---|---|---|---|---|---|---|
| Trezor Safe 7 | Best overall for verifiable self-custody | 87/100 | Hardware | Layered MCU and two Secure Elements, including TROPIC01 | On-device transaction approval | SLIP39 backup; supports BIP39 restoration | Public firmware, external chip research and documented vulnerability disclosures | Component-level attack and resolved authenticity-verification defect |
| Ledger Flex | Secure everyday multi-asset transactions | 86/100 | Hardware | EAL6+ Secure Element running Ledger OS | Secure touchscreen and Clear Signing for supported transactions | BIP39 phrase; optional Ledger Recovery Key | Chip assurance, security research and published vulnerability record | Resolved Ethereum Clear Signing bypass; partially closed firmware |
| BitBox02 Bitcoin-Only Edition | Dedicated Bitcoin savings | 83/100 | Hardware | Microcontroller and ATECC608B secure chip | Device-screen transaction confirmation | microSD backup or BIP39 recovery words | Open-source, reproducible firmware and documented external testing | Resolved bootloader and signing-related vulnerabilities in shared components |
| OneKey Pro 2 | Premium multi-chain hardware signing | 81/100 | Hardware | Four EAL6+ secure chips and safeOS 2 | On-device review, QR signing and SignGuard simulations | Recovery phrase; optional encrypted SeedCard | Keylabs hardware and firmware audit with production retest | Residual lower-severity findings and limited post-launch history |
| Rabby Wallet | Active EVM and DeFi transaction protection | 76/100 | Software, local-key configuration | Encrypted local key storage; optional hardware signer | Transaction simulation, allowance visibility and risk warnings | Recovery phrase or private-key backup | Coinspect version-specific tests and public audit repository | Host-device compromise, phishing detection gaps and harmful approvals |
| SafePal S1 | Budget QR-based hardware signing | 65/100 | Hardware, QR signing | Secure Element; chip certification varies by revision | Device-screen confirmation and QR transaction exchange | Recovery phrase; optional passphrase | Historical Kraken research; current full-stack retest not independently verified | Historical tamper findings, hardware revision differences and customer-data incident |
| ELLIPAL Titan 2.0 | Dedicated air-gapped multi-asset signing | 60/100 | Hardware, QR signing | Advertised EAL5+ secure chip and sealed enclosure | Offline device review and QR-based signing | BIP39 recovery phrase | Complete current-product audit and reproducible builds not independently verified | Limited firmware transparency and complete-system independent verification |
| Zengo | Seedless mobile wallet access | 59/100 | Mobile MPC | Distributed signing between phone and server infrastructure | App transaction review and Web3 warnings | Email, cloud Recovery File and configured authentication factors | Testing program disclosed; complete current reports not independently verified | Recovery portability and external service dependencies |
This guide is for educational purposes only and is not financial advice.
Some links in this guide may be affiliate links. If you choose to purchase a wallet or use a service through these links, we may earn a commission at no additional cost to you.
How We Ranked the Most Secure Crypto Wallets (Methodology)
Wallet security cannot be reduced to chip certifications, air-gapped connections or whether a wallet has suffered a hack. Our methodology evaluates private-key protection, transaction signing, firmware integrity, recovery resilience and security history so strength in one category cannot conceal weaknesses elsewhere.
The Coin Bureau Wallet Security Score
The Coin Bureau Wallet Security Score is a proprietary 100-point methodology based on documented security architecture, transaction verification, software transparency, recovery protections and incident history. The assessment reflects information available as of Nov. 4, 2026.
| Security Category | Weight |
|---|---|
| Private-key generation and protection | 20% |
| Transaction verification and scam resistance | 20% |
| Firmware/software integrity and transparency | 15% |
| Recovery resilience and portability | 15% |
| Security history and incident response | 15% |
| Independent testing and audit coverage | 10% |
| Secure defaults and operational usability | 5% |
Private-key protection covers entropy generation, key isolation and resistance to extraction. Transaction verification assesses trusted displays, clear signing, transaction simulations and scam warnings. Recovery resilience considers backup reliability, portability and dependence on third-party services, while firmware integrity evaluates source-code availability, update verification and reproducible builds.
Each category receives a grade from zero to five, converted into weighted points for a total score out of 100.
A wallet cannot earn a high security score simply by using an EAL-certified secure element or advertising an air-gapped design. Weak transaction verification, limited recovery options, insufficient independent testing or serious unresolved vulnerabilities can materially reduce its score.
What We Check and Where the Data Comes From
We use manufacturer security documentation, hardware architecture disclosures, firmware repositories, software release records, recovery specifications, vulnerability reports, independent audits and published penetration tests.
Independent material includes Coinspect's wallet-security tests, Ledger Donjon research and published audit findings. Donjon is operated by Ledger, so its findings on competing wallets are evaluated alongside technical evidence and manufacturer responses. Third-party testing is one input into the assessment, not the basis of the overall ranking.
We distinguish signed firmware updates from reproducible builds, and chip-level certifications from evaluations covering the complete wallet. Common Criteria EAL5+ or EAL6+ certification does not automatically establish end-to-end wallet security. Recovery methods, including BIP39, SLIP39 and multiparty computation (MPC), are assessed according to their portability, reliability and service dependencies.
What Our Security Score Cannot Guarantee
A high score cannot eliminate phishing, malicious transaction approvals, compromised devices, exposed recovery phrases, physical attacks or future vulnerabilities. A wallet may securely protect private keys while still allowing its owner to approve a transaction that drains their funds.
Open-source software does not guarantee that code has been independently reviewed, and an audit may cover only specific components or firmware versions. Similarly, hardware certifications cannot guarantee secure recovery practices or protection against every attack.
Most Secure Crypto Wallets Compared
Trezor and Ledger lead for owners who need broad hardware protection, while BitBox02 and Rabby serve more specific storage and transaction-review needs. Each wallet is evaluated for key protection, transaction security, recovery, independent verification and known vulnerabilities. The rankings distinguish hardware isolation, software-based transaction protection and recovery tradeoffs rather than treating every wallet as equally secure for every user.
1
Trezor Safe 7: Best Overall and for Open-Source Transparency
Security Score: 87/100
·
Best for: Transparent, long-term self-custody
Trezor Safe 7: Best Overall and for Open-Source Transparency
Why it ranks where it does. Trezor Safe 7 leads with 87/100 because it combines layered hardware protection, inspectable firmware and flexible recovery options. Its open-source approach supports independent scrutiny, although disclosed component and authenticity weaknesses reduce its score. Transaction interpretation is also less comprehensive than specialist DeFi signing interfaces.
Recovery and Backup. Trezor Safe 7 supports SLIP39 recovery, allowing owners to distribute backup shares and configure a recovery threshold. Restoration requires enough valid shares and compatible recovery software. BIP39 and SLIP39 are different formats, so owners must understand compatibility before selecting a backup. Losing the required recovery material can make funds inaccessible if the original device is also lost.
Independent Verification. Trezor publishes firmware source code that researchers can inspect and use for build verification. Research disclosed a June 2026 TROPIC01 attack that compromised one component without defeating the complete wallet architecture. Trezor separately corrected an authenticity-verification weakness involving proofs checked against a combined key set. These disclosures demonstrate active security scrutiny while reinforcing the need for verified updates.
2
Ledger Flex: Best Balance of Security and Everyday Usability
Security Score: 86/100
·
Best for: Secure everyday multi-asset management
Ledger Flex: Best Balance of Security and Everyday Usability
Why it ranks where it does. Ledger Flex ranks second with 86/100 because it combines strong key isolation with a secure touchscreen that makes transaction approval easier to inspect. Its everyday usability is a security advantage for owners regularly moving assets. Partially closed firmware and documented signing defects keep it just below Trezor Safe 7.
Recovery and Backup. Ledger Flex uses a conventional BIP39 recovery phrase, allowing restoration through compatible wallets. The optional Ledger Recovery Key provides a PIN-protected NFC backup but depends on compatible Ledger hardware. Ledger Recover is a separate optional recovery service involving additional provider and identity-verification assumptions. Owners should distinguish these options and securely preserve their chosen recovery route.
Independent Verification. Ledger publishes security documentation and operates a vulnerability research and disclosure program. Its Secure Element certification provides evidence about the evaluated chip, but not an audit of every wallet application. Ledger OS is only partially open-source. A disclosed Ethereum application Clear Signing bypass was fixed in version 1.22.3, demonstrating why coin application updates are necessary alongside device firmware updates.
3
BitBox02 Bitcoin-Only Edition: Best for Bitcoin-Only Security
Security Score: 83/100
·
Best for: Dedicated Bitcoin cold storage
BitBox02 Bitcoin-Only Edition: Best for Bitcoin-Only Security
Why it ranks where it does. BitBox02 Bitcoin-Only Edition scores 83/100 because it focuses on protecting Bitcoin with a smaller feature set, verifiable firmware and portable recovery. Removing altcoin support reduces code and transaction types requiring review. Serious repaired defects in shared components prevent a higher security-history score.
Recovery and Backup. Owners can back up the wallet using a microSD card or displayed BIP39 recovery words. Both provide recovery material that must be protected independently of the device. The microSD backup should be treated as a spending secret and stored securely. A device password protects access to the wallet but does not make an exposed backup harmless.
Independent Verification. BitBox02 publishes open-source firmware and supports reproducible builds, allowing researchers to compare distributed firmware with inspected source code. Signed firmware and device authentication checks help verify releases and hardware. Dixence documented 2026 security updates addressing bootloader and silent-payment risks. A separate Multi-edition memory flaw did not affect the Bitcoin-only edition, although shared-component findings remained relevant.
4
OneKey Pro 2: Best Premium Multi-Chain Hardware Wallet
Security Score: 81/100
·
Best for: Premium multi-chain hardware signing
OneKey Pro 2: Best Premium Multi-Chain Hardware Wallet
Why it ranks where it does. OneKey Pro 2 earns 81/100 for combining hardware-isolated signing with detailed transaction review and flexible QR workflows. Its October 8, 2026 launch means independent production testing is available, but its longer-term operating record remains limited. Residual audit findings and feature complexity keep it below established rivals.
Recovery and Backup. OneKey Pro 2 retains a phrase-based recovery route for restoring wallet access. The optional SeedCard provides an encrypted, PIN-protected backup but introduces compatible-device requirements. Owners should understand how to restore funds without relying solely on an accessory and should securely preserve their standard recovery material.
Independent Verification. Keylabs assessed the hardware, firmware and threat model and conducted a production retest. Production firmware 1.0.0 fixed identified medium-severity weaknesses involving signing confirmation, rollback enforcement and MCU-to-Secure Element communication. Lower-severity and partially mitigated findings remained. OneKey also references SlowMist, but the older SlowMist audit announcement does not establish complete coverage of Pro 2 and safeOS 2.
5
Rabby Wallet: Best Hot Wallet for DeFi Transaction Protection
Security Score: 76/100
·
Best for: Active EVM and DeFi users
Rabby Wallet: Best Hot Wallet for DeFi Transaction Protection
Why it ranks where it does. Rabby scores 76/100 for its strong transaction simulation and approval controls. Its ability to show expected balance changes, allowances and contract interactions addresses common DeFi signing risks. However, a browser-wallet configuration with locally stored keys remains exposed to the security of the connected computer.
Recovery and Backup. Conventional Rabby accounts depend on a securely stored recovery phrase or private-key backup. Losing the backup and access to the original wallet can make funds unrecoverable. Hardware-wallet integration provides an alternative signing arrangement, but only when the keys were generated securely on the hardware device. Importing an previously exposed software-wallet seed into hardware does not restore its secrecy.
Independent Verification. Rabby publishes source code and an audit repository. Coinspect evaluated Chrome extension version 0.93.88 and verified transaction simulation and detailed approval prompts. Its assessment also documented security gaps, including a missed sign-in domain mismatch and inconsistent phishing detection. These findings support specific implemented features, not a guarantee against malicious transactions.
6
SafePal S1: Best Budget Air-Gapped Wallet
Security Score: 65/100
·
Best for: Affordable QR-based hardware signing
SafePal S1: Best Budget Air-Gapped Wallet
Why it ranks where it does. SafePal S1 receives 65/100 because it offers hardware-isolated QR signing and a standard recovery route at a relatively low price. However, limited firmware transparency, hardware revision differences and incomplete current independent verification keep it below higher-ranked devices.
Recovery and Backup. SafePal S1 uses a recovery phrase with an optional passphrase for restoring wallet access. The recovery material must remain secure and available independently of the device. Losing the required phrase or forgetting an additional passphrase can permanently prevent restoration. Routine signing uses QR codes, while firmware installation follows a separate official USB update procedure.
Independent Verification. SafePal documents device authentication and tamper-response protections, but a complete current-revision independent hardware retest was not verified for this assessment. Kraken's historical SafePal S1 research identified tamper-detection and firmware downgrade weaknesses without demonstrating theft of customer funds. Older findings should not automatically be applied to every revised device, but they remain relevant to its security history.
7
ELLIPAL Titan 2.0: Best Dedicated Air-Gapped Multi-Asset Workflow
Security Score: 60/100
·
Best for: Offline QR signing across multiple assets
ELLIPAL Titan 2.0: Best Dedicated Air-Gapped Multi-Asset Workflow
Why it ranks where it does. ELLIPAL Titan 2.0 earns 60/100 because its dedicated offline QR workflow eliminates routine USB data, Bluetooth and Wi-Fi connections during signing. Its hardware protections and standard recovery are useful, but limited independent firmware verification and complete-product testing reduce confidence in its overall security.
Recovery and Backup. ELLIPAL Titan 2.0 uses BIP39 recovery words that can restore access through compatible wallet software or hardware. Owners should store the phrase offline and verify recovery before relying on the device for long-term storage. Firmware updates use a microSD card and adapter. Importing the hardware wallet's recovery phrase into a phone exposes the same keys to the phone's security environment.
Independent Verification. ELLIPAL describes its Secure Element, sealed enclosure and air-gapped signing architecture. However, this assessment did not independently verify a complete current firmware audit or reproducible distributed builds. An offline update process does not itself prove firmware authenticity or transaction parser security. These areas require evidence beyond the absence of wireless connectivity.
8
Zengo: Best MPC-Based Mobile Wallet
Security Score: 59/100
·
Best for: Mobile users avoiding seed phrases
Zengo: Best MPC-Based Mobile Wallet
Why it ranks where it does. Zengo scores 59/100 because its multi-party computation architecture reduces dependence on a conventional recovery phrase. This can help users avoid common seed-backup mistakes. However, its service-dependent recovery model, limited portability and incomplete independent verification of current testing scope reduce its score against more self-contained hardware wallets.
Recovery and Backup. Zengo's recovery model uses account verification, a cloud Recovery File and biometric authentication options. Its broader 3FA description includes email, the Recovery File and 3D FaceLock, although newer account recovery instructions describe two mandatory factors with FaceLock recommended or required for selected Pro features. Users must verify their configured requirements. Losing essential account and Recovery File access can defeat recovery.
Independent Verification. Zengo describes annual independent penetration testing and an established security program. However, complete current reports and their detailed findings were not independently verified for this assessment. ISO 27001 provides evidence about security management processes rather than proving that every wallet implementation is free of vulnerabilities. The independently operated Guaranteed Access system offers a company-failure contingency, but remains dependent on defined infrastructure and trustee processes.
Which Crypto Wallet Security Model Is Safest?
Hardware wallets are generally strongest against online private-key theft. Software transaction warnings can better explain risky interactions, while recovery design determines whether theft or accidental loss becomes the larger concern.
| Main Threat | Stronger Starting Model | What Remains Exposed |
|---|---|---|
| Malware stealing signing secrets | Dedicated hardware with a fresh hardware-generated seed | Harmful approvals and exposed backups |
| Deceptive DeFi transactions | Simulation plus independently verified hardware signing where supported | Detection gaps and contract behavior |
| Loss of a single device | Tested portable backup or well-designed recovery factors | Loss or theft of the backup itself |
| One compromised signer | Properly configured multisig | Shared software flaws and recovery complexity |
| Cable/radio attack paths | QR-based signing | QR parsers, firmware and signing mistakes |
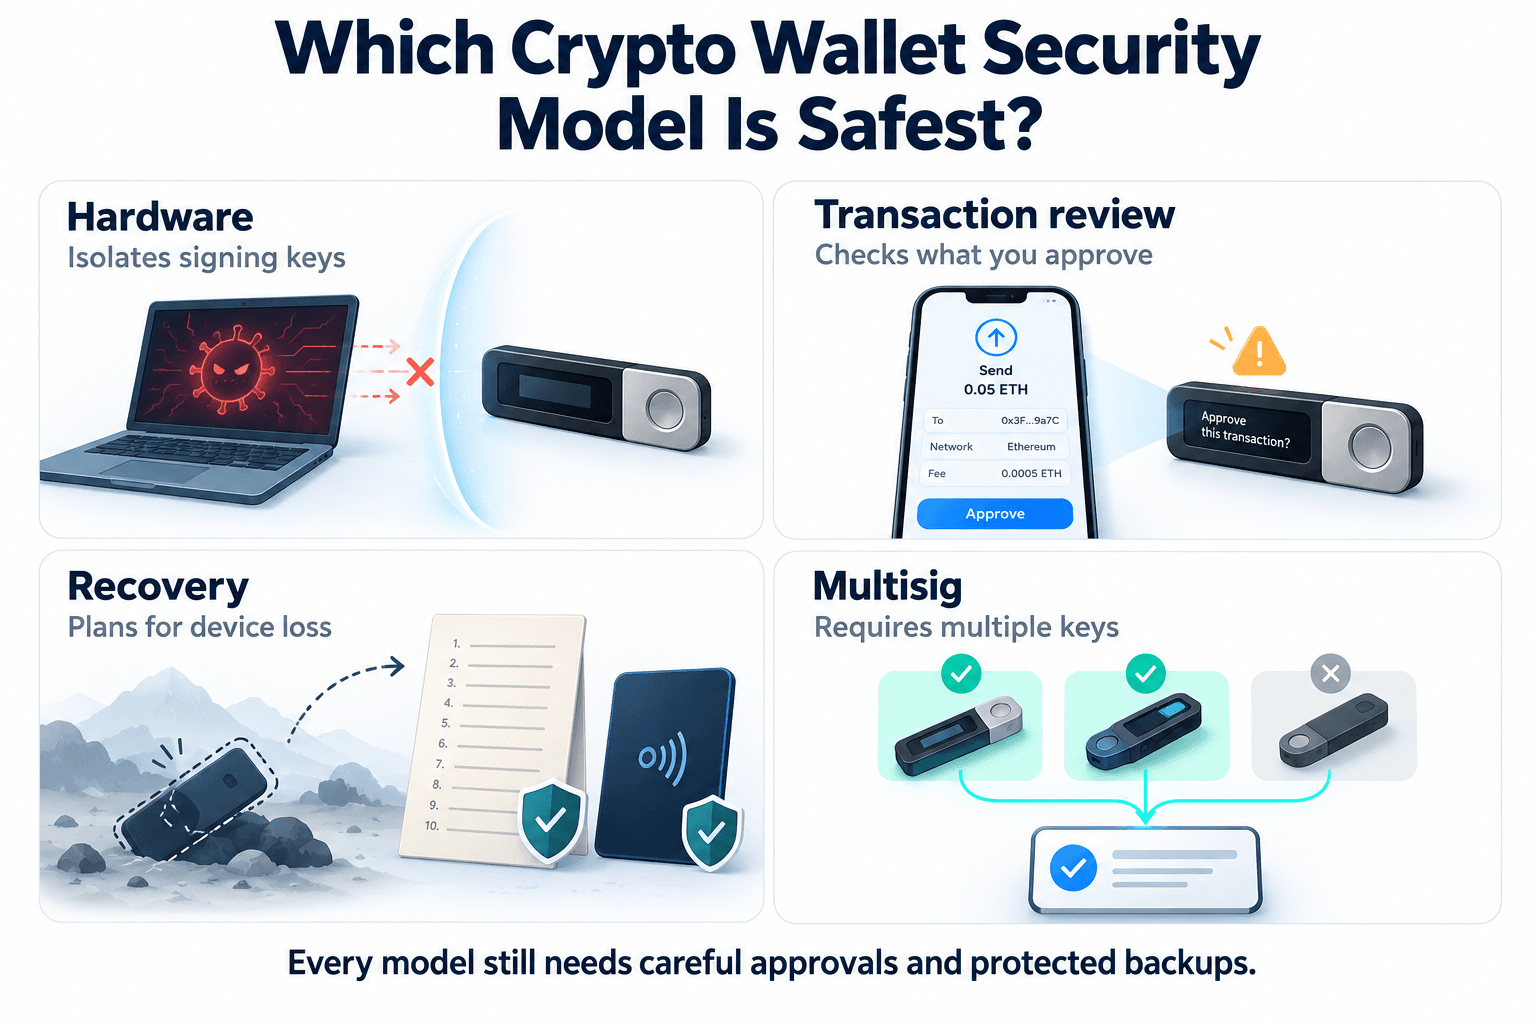 Key Isolation And Recovery Design Determine Your Security Tradeoffs
Hardware Wallets vs Software Wallets: Which Offers Stronger Protection?
Hardware provides stronger isolation from malware on the everyday computer or phone. A conventional software wallet stores and uses its signing secret within that general-purpose environment, so a compromised host can threaten the secret directly.
Hardware can faithfully sign a malicious authorization that its owner confirms, while software simulations may identify the harmful result before approval. For savings, favor hardware-generated accounts with tested backups; for frequent Web3 use, combine good transaction interpretation with a separate signer where supported and keep spending balances limited.
Our hardware vs software wallet comparison explores that division. The practical choice starts with the threat you need to reduce.
Also Read
Air-Gapped vs USB vs Bluetooth: Does Connectivity Affect Security?
Air-gapped QR signing removes direct USB and radio communication from the signing workflow. USB introduces a host-device protocol, while Bluetooth adds wireless transport and pairing behavior; encrypted Bluetooth is not inherently equivalent to exposing private keys.
Every method still moves untrusted transaction information into the signer. QR parsers can contain bugs, and a cable-connected device can enforce strong signing boundaries. Firmware integrity and accurate display of the signed action can be more consequential than connection type alone.
Seed Phrase vs Seedless Recovery: Which Is Safer?
A standard seed phrase offers broad portability but gives an attacker a powerful recovery secret. SLIP39 shares distribute backup risk through a threshold, while NFC cards and MPC replace phrase handling with different possession or authentication requirements.
Each recovery method trades one failure mode for another. A portable phrase can be stolen, a threshold backup can lose too many shares and a seedless account can lose required recovery factors. Plan around the failures below before depositing funds.
| Failure Scenario | BIP39 Phrase | SLIP39 Shares | Seedless NFC Cards | Mobile MPC |
|---|---|---|---|---|
| Device is lost | Restore with phrase and any passphrase | Restore with required share threshold and any passphrase | Use a configured backup card | Recover with required account factors |
| Recovery phrase is stolen | Funds exposed unless an effective separate passphrase protects them | One share below threshold is insufficient | No phrase in pure seedless mode | No conventional phrase |
| All backup cards are lost | Phrase remains usable | Required shares remain usable | No recovery if no card or separate phrase exists | Cards are not the recovery method |
| Recovery service disappears | Compatible independent tools can restore | Compatible SLIP39 tools can restore | Existing functioning cards may work with compatible software | Requires the provider’s independent contingency route |
| Phone and associated accounts are lost | Offline backup can restore elsewhere | Offline shares can restore elsewhere | Card and credentials remain necessary | Surviving configured email/cloud/biometric factors are needed |
A multi-signature wallet distributes authorization across several keys. It can reduce single-key theft risk, but adds backup and inheritance complexity. Keeping a written restoration plan is part of that protection.
What Security Risks Can Compromise Even the Safest Crypto Wallet?
Weak seed generation, exploitable firmware and harmful approvals can defeat otherwise strong hardware. Evaluate the demonstrated attack and affected version before treating a product as safe or compromised.
A stolen customer address can make phishing more targeted, while a component-level laboratory finding may require further attacks before funds become accessible. Confirmed private-key compromise gives an attacker a direct spending route. Our hardware-wallet security threats guide separates these attack paths and the protections relevant to each.
Firmware Vulnerabilities and Real-World Wallet Security Incidents
COLDCARD’s July disclosure and Trezor’s June disclosure demonstrate two very different failure modes. The former involved exploitable seed generation and confirmed losses; the latter showed a difficult attack against one chip without demonstrating full-wallet access.
| Wallet | Disclosure Date | Affected Component or Version | Attack Conditions | Confirmed Losses | Remediation | Remaining User Action |
|---|---|---|---|---|---|---|
| COLDCARD | July 30, 2026 | Seeds generated on affected firmware; model/track matrix applies | Attackers regenerate weak keys offline; no device takeover needed | Manufacturer confirms theft | Fixed generation firmware and seed-migration guidance | Update and migrate affected funds unless a documented exception applies |
| Trezor Safe 7 | June 3, 2026 | TROPIC01 firmware-verification boundary | Physical chip preparation and specialist laser-fault equipment | No full-wallet theft demonstrated in the cited disclosure | Coordinated component disclosure; other barriers remain | Follow current advisories and updates; June disclosure required no seed migration |
Coinkite’s July 30 advisory confirms that attackers regenerated weak private keys offline and stole funds. The failure concerned entropy used to create the seed, so owning a physical device was unnecessary once attackers could reproduce the secret.
Updating firmware corrects future generation but cannot make an existing weak seed unpredictable. The current security-status page lists fixed releases and migration requirements, with narrowly documented exceptions for independently added entropy. Its subsequent release record includes further signing and update checks, while independent validation covers specific repairs rather than every possible flaw.
The Trezor case involved a laser attack against TROPIC01’s firmware checks. Running custom chip firmware exposed component secrets, but the PIN and wallet backup still depended on other protections. Trezor’s June 3 response described a component vulnerability without a demonstrated full-wallet compromise.
The user action depends on what failed. Weakly generated seeds require new recovery material and on-chain migration; a repaired firmware defect may require an update without replacing the seed. Chip certification alone cannot tell an owner which response applies.
Malicious Transactions, Blind Signing and Smart-Contract Approvals
A wallet can lose funds while its private keys remain secret. An ordinary transfer authorizes movement to a recipient; a token allowance authorizes a spender contract to move specified tokens, potentially later.
Unlimited allowances extend that authority to a large amount. Malicious signatures can also grant spending permissions or account control, so a request labeled as verification or login deserves the same care as a visible transfer. Blind signing removes readable context when the device cannot interpret the request.
Clear Signing translates supported actions into readable details, while simulation estimates execution results. Neither can guarantee safe smart contract behavior. Verify recipients, amounts and permissions on the hardware display; a trustworthy phone preview cannot compensate for a different action shown by the signer.
Fake Wallets, Compromised Apps and Recovery-Phrase Theft
Counterfeit devices and unofficial downloads can substitute an attacker-controlled setup or signing interface. Packaging is weak evidence because it can be copied; supported device authentication and genuine firmware checks provide a stronger starting point.
Fake support agents often ask owners to enter recovery words to fix an alleged problem. Once the actual recovery secret is exposed, the attacker may restore the wallet independently of its hardware or PIN. Our hardware-wallet mistakes guide covers the operational failures that undermine otherwise credible designs.
How to Set Up and Use a Crypto Wallet Securely
Start with authentic hardware and software, then ensure that recovery works before making a large deposit. Keep daily signing activity separate from savings so one bad DApp interaction has a limited reach.
Complete the setup and recovery checks before adding a meaningful balance. Once funded, keep software current and review permissions every time you transact; our crypto safety guide also covers account and device protections around that routine.
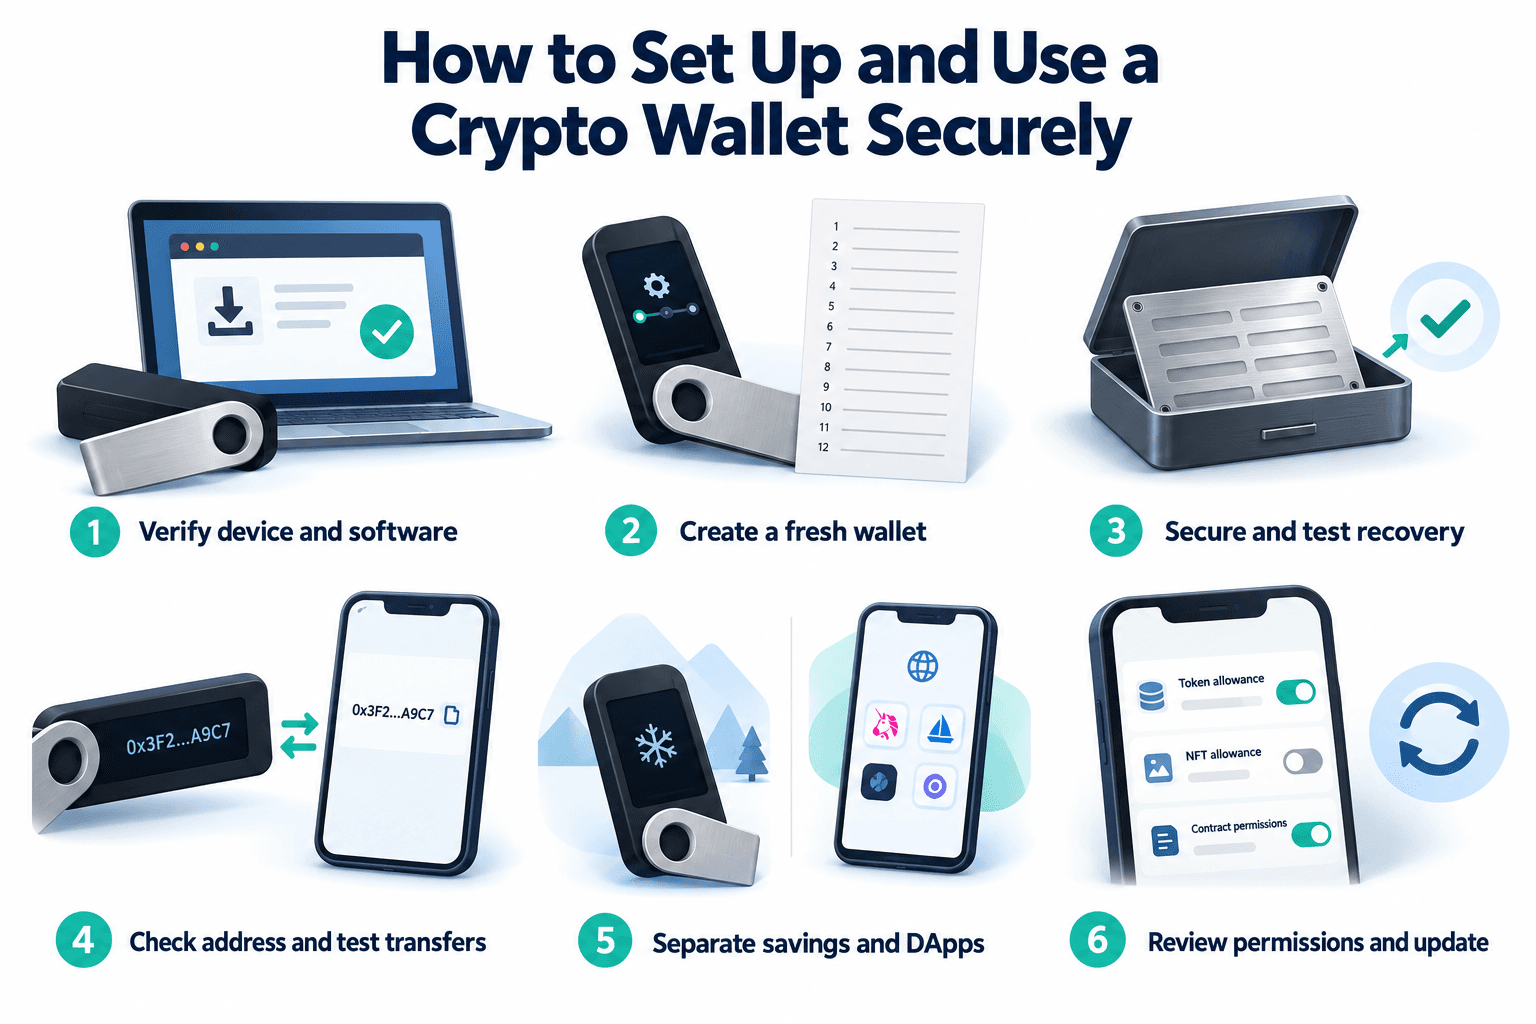 Safer Wallet Setup Starts With Verification And Tested Backups
Verify the Device and Firmware Before Depositing Funds
- Buy from the manufacturer or an authorized seller, and reach downloads through the official domain.
- Run the supported device-authentication check rather than relying on seals or packaging.
- Install genuine wallet software and current firmware through official verification procedures. Update coin apps where applicable.
- Generate a fresh wallet through the trusted setup process. Reject a prefilled recovery phrase or a device someone else initialized.
- Verify the receiving wallet address on the device and make a small test deposit and outgoing transfer before moving a meaningful balance.
Protect Your Recovery Method and Test It
Keep recovery phrases offline in secure storage, preferably separate from the device. Do not photograph or upload them. For cards or MPC, protect every required backup object and account factor rather than assuming that seedless means backup-free.
Use the manufacturer’s supported backup-check process or test recovery with an unfunded setup. Avoid typing a live hardware-wallet seed into general-purpose software. Confirm the recovered addresses and retain any account information needed for restoration.
An optional BIP39 passphrase can protect against theft of the base phrase, while a threshold backup can distribute disaster risk. Both also introduce additional ways to lock yourself out. Use advanced arrangements only when you can document and repeat the recovery process reliably.
Separate Savings From Daily DApp Activity
Create a dedicated savings wallet and a separate account or wallet for frequent DApp interactions. Distinct recovery roots provide stronger separation against seed compromise; different addresses under the same seed do not provide that separation.
Review transaction details and permissions before every signature. Limit token allowances when practical and revoke permissions you no longer need. Keep the phone, computer and wallet software updated so old defects do not remain in your signing workflow.
A watch-only wallet can monitor balances without loading spending keys onto an everyday device. Protect extended public keys too because they can expose account activity and reduce privacy.
Secure Wallet Setup Checklist
- Official purchase and download channels verified.
- Device authentication and software updates completed.
- Fresh wallet created without a prefilled backup.
- Recovery method secured and tested.
- Device address and small transfers checked.
- Savings separated from DApp spending.
- Permissions reviewed and unused allowances removed.
- Optional passphrase or threshold setup documented if used.
Final Verdict: Which Secure Crypto Wallet Should You Choose?
Trezor Safe 7 is our most secure crypto wallet overall because it combines layered hardware protection, inspectable firmware and flexible recovery options. Ledger Flex is the strongest alternative for users who prioritize secure, everyday multi-asset transactions, while BitBox02 Bitcoin-Only Edition is our preferred choice for dedicated Bitcoin storage.
Rabby stands out for active DeFi users who need transaction simulations and approval warnings. ELLIPAL Titan 2.0 offers a dedicated air-gapped signing experience, while SafePal S1 provides a more affordable hardware option. Zengo is worth considering for users who prefer seedless recovery, although its MPC architecture introduces additional service dependencies.
No crypto wallet eliminates every security risk. Choose a wallet based on how it protects private keys, verifies transactions and supports recovery, not on hardware certifications or security scores alone.