A hardware wallet is a physical device that keeps the cryptographic secrets used to control cryptocurrency isolated from an internet-connected computer or phone. Your crypto stays on the blockchain. When you send funds or interact with a DApp, wallet software prepares the transaction, the hardware wallet verifies and signs it internally, and the signed transaction is returned for broadcast.
That segregation of duties explains most of what makes a hardware wallet useful. The computer or smartphone handles the interface, network connection and much of the transaction preparation. The hardware device controls authorization. Modern designs increasingly add another job: showing enough information on a trusted display for the user to understand what is being authorized before the signature is created.
Editor's Note (Sept. 30, 2026): We fully updated and restructured this guide in September 2026 to reflect how hardware-wallet security and recovery have evolved. The new version adds a step-by-step explanation of transaction signing, clearer distinctions between hardware wallets, cold storage and air-gapped wallets, deeper coverage of Secure Elements, seed phrases, passphrases and newer backup models, plus expanded guidance on blind signing, clear signing, smart-contract risks and using hardware wallets with interfaces such as MetaMask and Rabby.
How Do Hardware Wallets Work? Quick Verdict
A hardware wallet is a dedicated signing device that keeps the secrets used to authorize crypto transactions separated from an everyday phone or computer. Your crypto remains on the blockchain. The device protects signing authority, verifies transaction details and creates signatures without needing to expose the private key to the connected host.
Hardware Wallet Key Points
-
Your crypto is not stored inside the hardware wallet Coins and tokens remain recorded on their blockchains. The device protects the cryptographic secrets used to control the associated accounts.
-
The private key does not need to leave the device Wallet software prepares a transaction, the hardware wallet signs it internally after approval, and the signed transaction is returned for broadcast.
-
The device screen is part of the security model A trusted display lets you verify addresses, amounts and supported transaction details independently of a potentially compromised computer or phone.
-
Recovery information is more important than the physical device A lost or broken wallet can usually be replaced if the required recovery phrase, shares or other backup credentials are still available.
-
A hardware wallet cannot make a bad transaction safe Phishing, malicious DApp approvals, wrong recipients and stolen recovery phrases can still cause losses even when the private key itself remains protected.
-
Hardware wallets are best viewed as one layer of self-custody security Strong protection combines key isolation with reliable backups, trusted setup, transaction verification, current firmware and careful signing behavior.
Disclaimer
This guide is for educational purposes only.
Disclosure
Some links in this guide may be affiliate links. If you choose to use a service through these links, we may earn a commission at no additional cost to you.
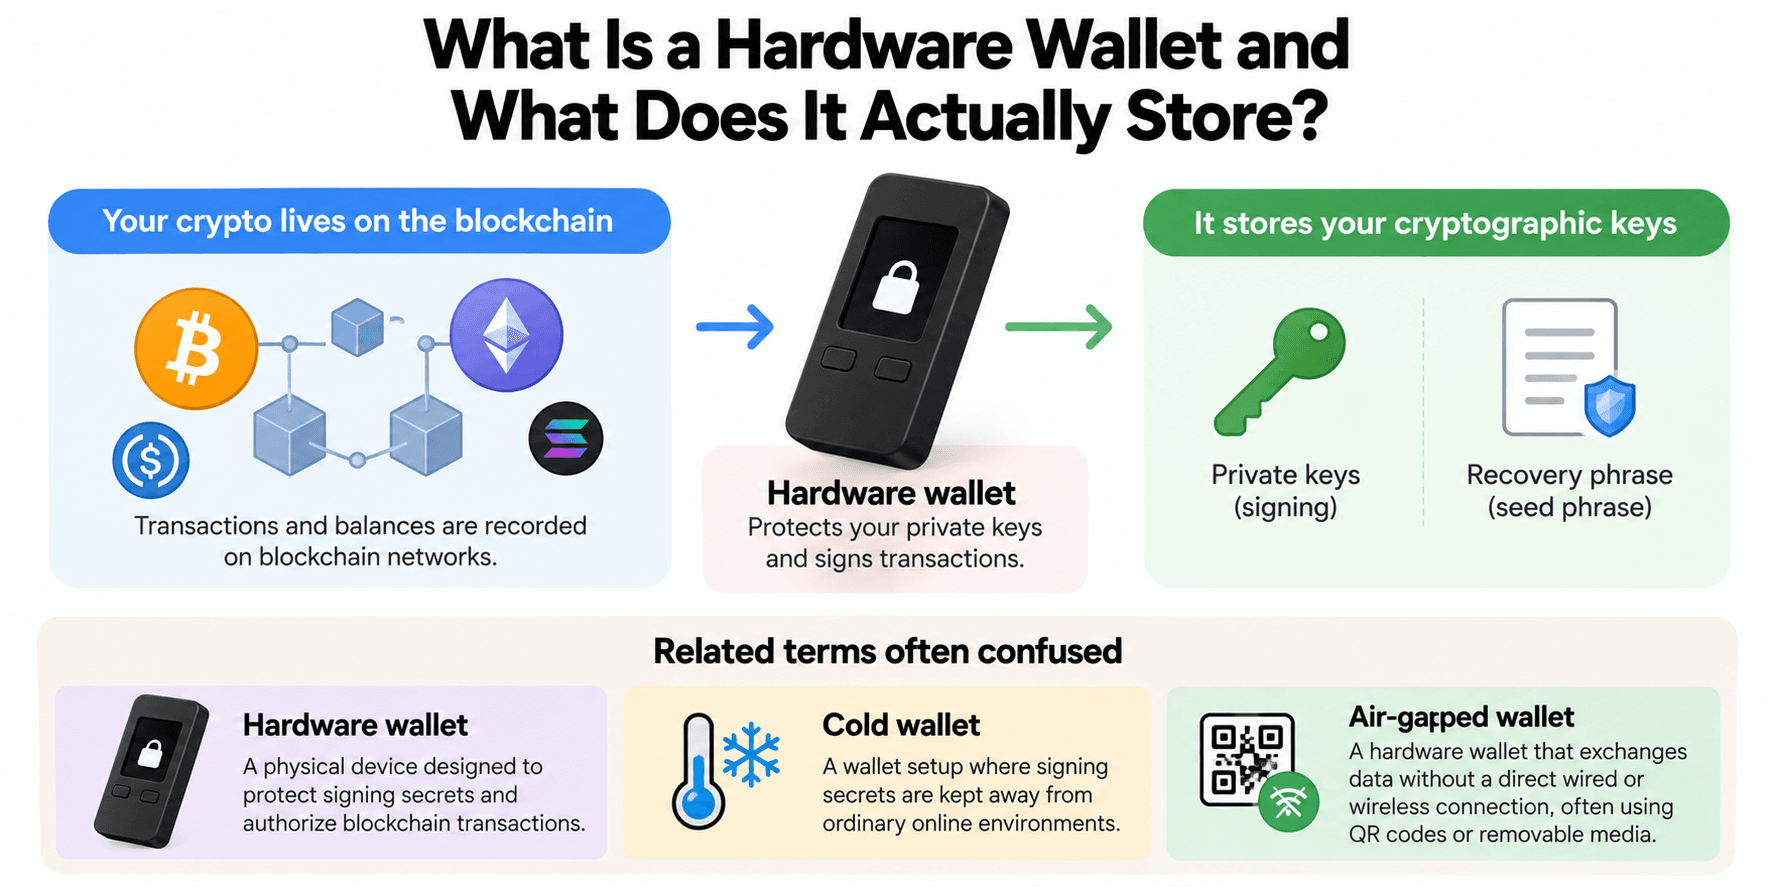
What Is a Hardware Wallet and What Does It Actually Store?
A hardware wallet is a dedicated signing device. It protects the cryptographic secrets that control blockchain accounts while keeping those secrets separated from everyday computers and phones.
 Understanding What Hardware Wallets Actually Store and Protect
Your Crypto Does Not Live Inside the Hardware Wallet
Coins and tokens are records maintained by their respective blockchains. A wallet gives you control over the credentials needed to authorize transactions involving those records.
That means a Bitcoin balance does not sit inside a small piece of hardware waiting to be plugged in. The Bitcoin network records the relevant transaction outputs. Ethereum and other account-based chains maintain their own blockchain state. The wallet controls the keys associated with the addresses that can move those assets.
This difference also explains why losing the physical wallet does not automatically destroy the crypto. If the recovery information still exists and is compatible with another wallet, the underlying keys can be regenerated and access restored.
Think of the hardware device less like a safe containing coins and more like a specialized authorization machine. The analogy only goes so far, though. A physical key opens one lock. A modern deterministic crypto wallet can derive an entire tree of blockchain accounts from the same underlying secret.
What the Device Actually Protects
Hardware wallets protect secret cryptographic material used to derive or access private keys and generate valid transaction signatures.
The exact implementation varies. Some devices place sensitive material inside a Secure Element. Others combine a main microcontroller with dedicated security chips, and some split security responsibilities across several components. Trezor, for example, currently uses different chip architectures across its Safe range, including models where Secure Elements handle specific security functions alongside the main processor.
A wallet address sits at the public end of this system. It can be shared to receive funds. The secret signing material must remain private.
Hardware Wallet vs Cold Wallet vs Air-Gapped Wallet
- Hardware wallet: A physical device designed to protect signing secrets and authorize blockchain transactions.
- Cold wallet: A wallet setup where signing secrets are kept away from ordinary online environments.
- Air-gapped wallet: A hardware wallet designed to exchange transaction information without a direct wired or wireless data connection, often using QR codes or removable media.
A hardware wallet can form part of a cold-storage setup, although hardware and cold storage are not perfect synonyms. An air gap describes the communication architecture. It does not, by itself, settle every security question about the device.
Check out our top picks for the best hardware wallets. If you're on a budget, here are our picks for hardware wallets under $100.
How Do Hardware Wallets Work? The Transaction Process Step by Step
Hardware-wallet signing follows a simple sequence: create → transmit → verify → sign → return → broadcast.
Different blockchains encode transactions differently, but the separation between the online interface and protected signer is broadly similar.
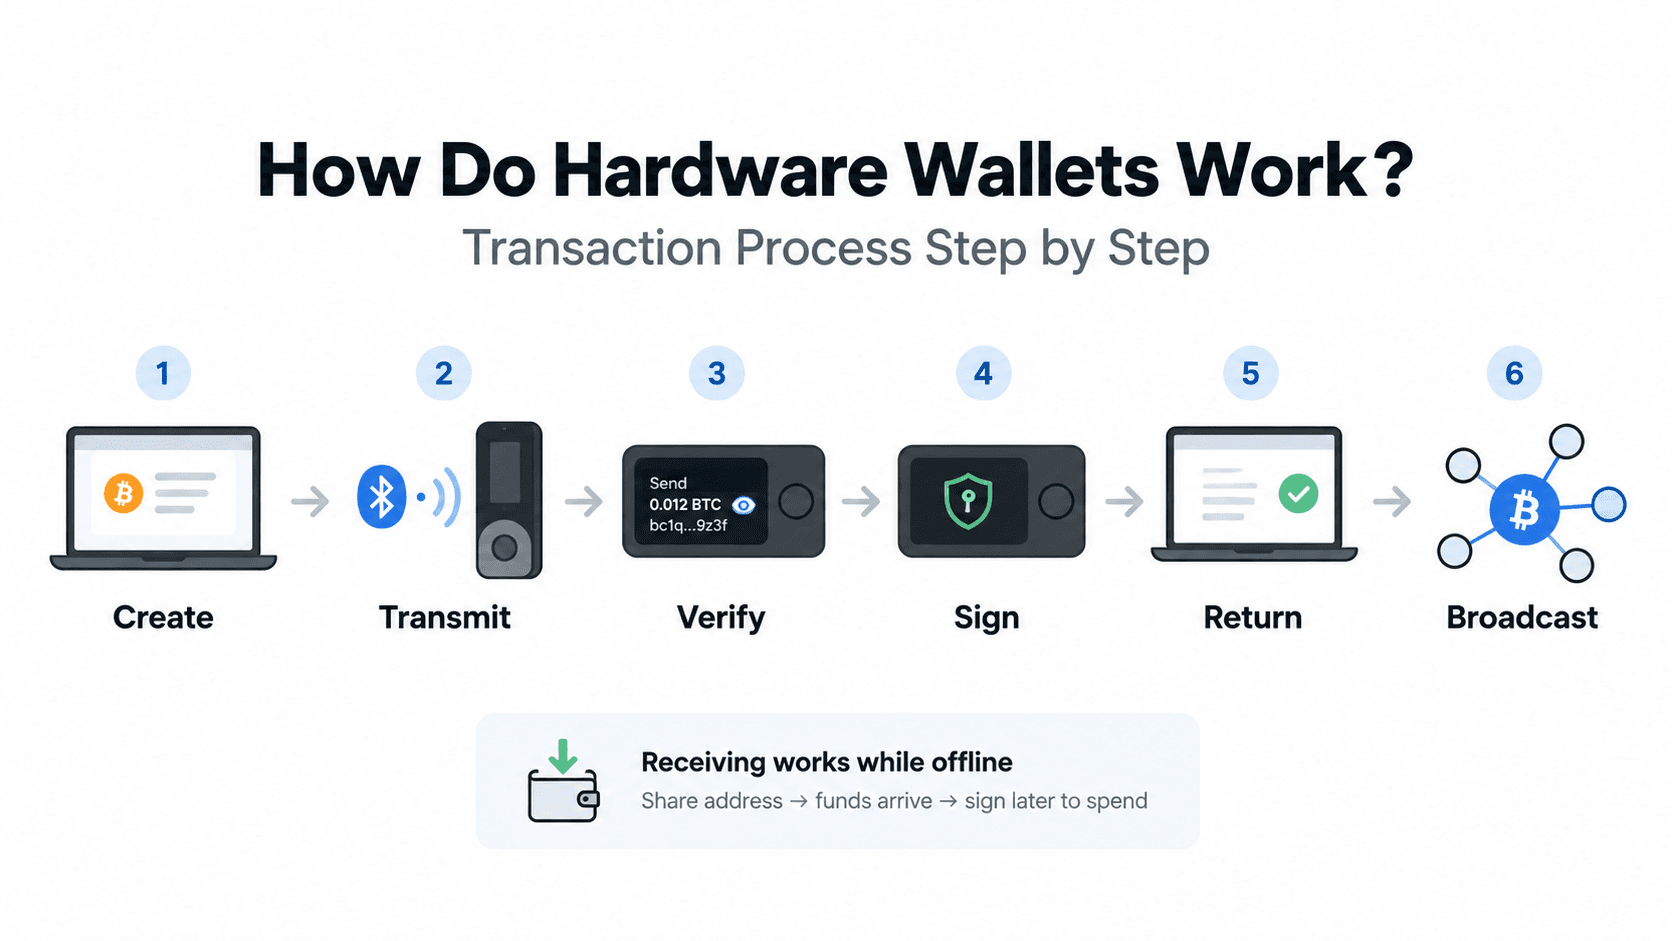 How Hardware Wallets Sign and Broadcast Crypto Transactions
Step 1: Wallet Software Creates an Unsigned Transaction
Suppose you want to send crypto to another address. You open compatible wallet software and enter the recipient address, amount and the required network fee.
The phone or computer then constructs an unsigned transaction containing the information the blockchain needs. It can prepare this request without possessing the private key that will ultimately authorize it.
A Bitcoin transaction and an Ethereum transaction are structurally different, so the exact fields vary by network. The user-facing flow remains familiar: construct an instruction first, obtain authorization second.
Network fees are also separate from the hardware wallet itself. They belong to the blockchain transaction being submitted.
Step 2: The Transaction Is Sent to the Hardware Wallet
The unsigned transaction now has to reach the signer.
Depending on the wallet, that communication can happen through USB, Bluetooth, NFC, QR codes or removable media. These methods create different usability and engineering trade-offs, but sending transaction data into the device does not require sending the private key out.
That separation is the core security boundary.
The computer says, in effect, "sign this transaction." The hardware wallet receives the request and decides whether to produce the required cryptographic signature after user approval.
Step 3: The Hardware Wallet Shows What You Are About to Sign
This is where a screen becomes more than a convenience feature.
A compromised computer could potentially manipulate what appears in wallet software. Clipboard malware could substitute an address, malicious software could prepare different transaction data, or an infected interface could simply misrepresent the request.
A hardware wallet with an independent trusted display can show transaction information from inside the signing environment. The user can compare the recipient, amount and other relevant details before giving approval.
Some Trezor devices, for example, display transaction details and require physical confirmation on the hardware itself, allowing users to verify information without relying entirely on the connected host.
The screen therefore has a security job, which is, provide an independent place to inspect the request that is about to receive your signature.
Step 4: The Device Signs the Transaction Internally
Once you approve the transaction, the hardware wallet uses the relevant private key to create a digital signature.
A digital signature proves that the appropriate signing authority approved the transaction. The blockchain can verify that signature without learning the private key itself.
The crucial movement here is easy to miss because very little appears to happen on screen.
The transaction enters the signing device. The private key does not need to leave it. The hardware wallet performs the cryptographic operation internally and produces the signature required by the network.
Step 5: The Signed Transaction Is Returned and Broadcast
The signed transaction is sent back to the companion wallet on the phone or computer.
That software can now broadcast it to the relevant blockchain network. Nodes receive the transaction, and the network's validators, miners or other consensus participants process it according to that blockchain's rules.
The hardware wallet has finished its main job once signing is complete. It generally does not need to remain connected while the network processes or confirms the transaction.
The blockchain remains the system recording the transaction and subsequent ownership state. The hardware signer authorizes the change.
How Receiving Crypto Works When the Hardware Wallet Is Offline
Receiving crypto is simpler because an incoming transfer does not require the recipient to sign anything.
Someone sending you funds only needs a valid receiving address. Your hardware wallet can be disconnected, switched off or sitting in a drawer while the transfer takes place.
The blockchain records the incoming transaction. Wallet software can later check the relevant addresses and show the updated balance.
The device becomes necessary when you need to authorize something with the secret key, such as spending the received funds.
For higher-value transfers, it is still sensible to verify the receiving address on the hardware device before sharing it. That protects against a compromised computer showing you an address controlled by somebody else.
How Seed Phrases, Private Keys, Public Keys and Wallet Addresses Fit Together
A hardware wallet can manage many blockchain accounts because modern wallets usually derive a hierarchy of keys from common underlying secret material.
The cleanest way to picture that relationship is:
Recovery phrase → seed → private keys → public keys → addresses
The precise derivation rules vary across wallets and blockchains, but this hierarchy explains why one backup can restore far more than one address.
Recovery Phrase → Seed → Private Keys
Many hardware wallets use mnemonic recovery systems built around standards such as BIP-39 and hierarchical key derivation based on BIP-32. BIP-39 defines a mnemonic system that can generate a binary seed, while BIP-32 defines a way to derive a tree of keys from a single seed.
Conceptually, the flow works like this:
- Recovery information represents or produces the wallet's underlying secret seed.
- The seed deterministically generates many private keys.
- Those keys control the accounts and addresses created along defined derivation paths.
"Deterministically" is the useful word. Given the same starting secret and the same derivation rules, compatible wallet software can reproduce the same keys.
That is why one recovery backup can restore many accounts rather than acting as a backup for one address at a time.
Private Keys, Public Keys and Addresses Are Different Things
Private keys, public keys and wallet addresses are related, but they serve different jobs.
- Private key: Secret information used to authorize transactions.
- Public key: Cryptographic information derived from the private key that can be used in signature verification.
- Wallet address: A blockchain-specific identifier usually derived from public-key information or related account data.
Sharing a wallet address therefore does not reveal the private key needed to spend from it.
The exact address-generation process depends on the network. Bitcoin, Ethereum and other blockchains use different address formats and derivation rules, which is why it is safer to understand the hierarchy than assume every chain transforms keys in exactly the same way.
How Wallet Software Can Show Your Accounts Without Holding the Private Keys
A wallet app does not need your private key simply to observe a public blockchain.
It can track addresses and query blockchain data to display balances, transaction history and incoming transfers. Some wallet architectures also expose extended public information that allows software to derive or monitor groups of public addresses without gaining spending authority.
BIP-32, for example, supports extended public keys, commonly referred to in Bitcoin contexts as xpubs, that can derive certain descendant public keys without exposing the corresponding private keys.
That creates a useful split: wallet software can remain useful for monitoring while the hardware wallet stays disconnected. Spending still requires access to the signing secret.
Why Is a Hardware Wallet Safer Than Keeping Keys on a Phone or Computer?
Hardware wallets reduce private-key exposure by moving signing into a device built for a much narrower security job.
A general-purpose laptop or smartphone has to do almost everything. It runs a browser, extensions, messaging software, downloads, applications and background services. Every additional component creates another possible path for malicious code or human error.
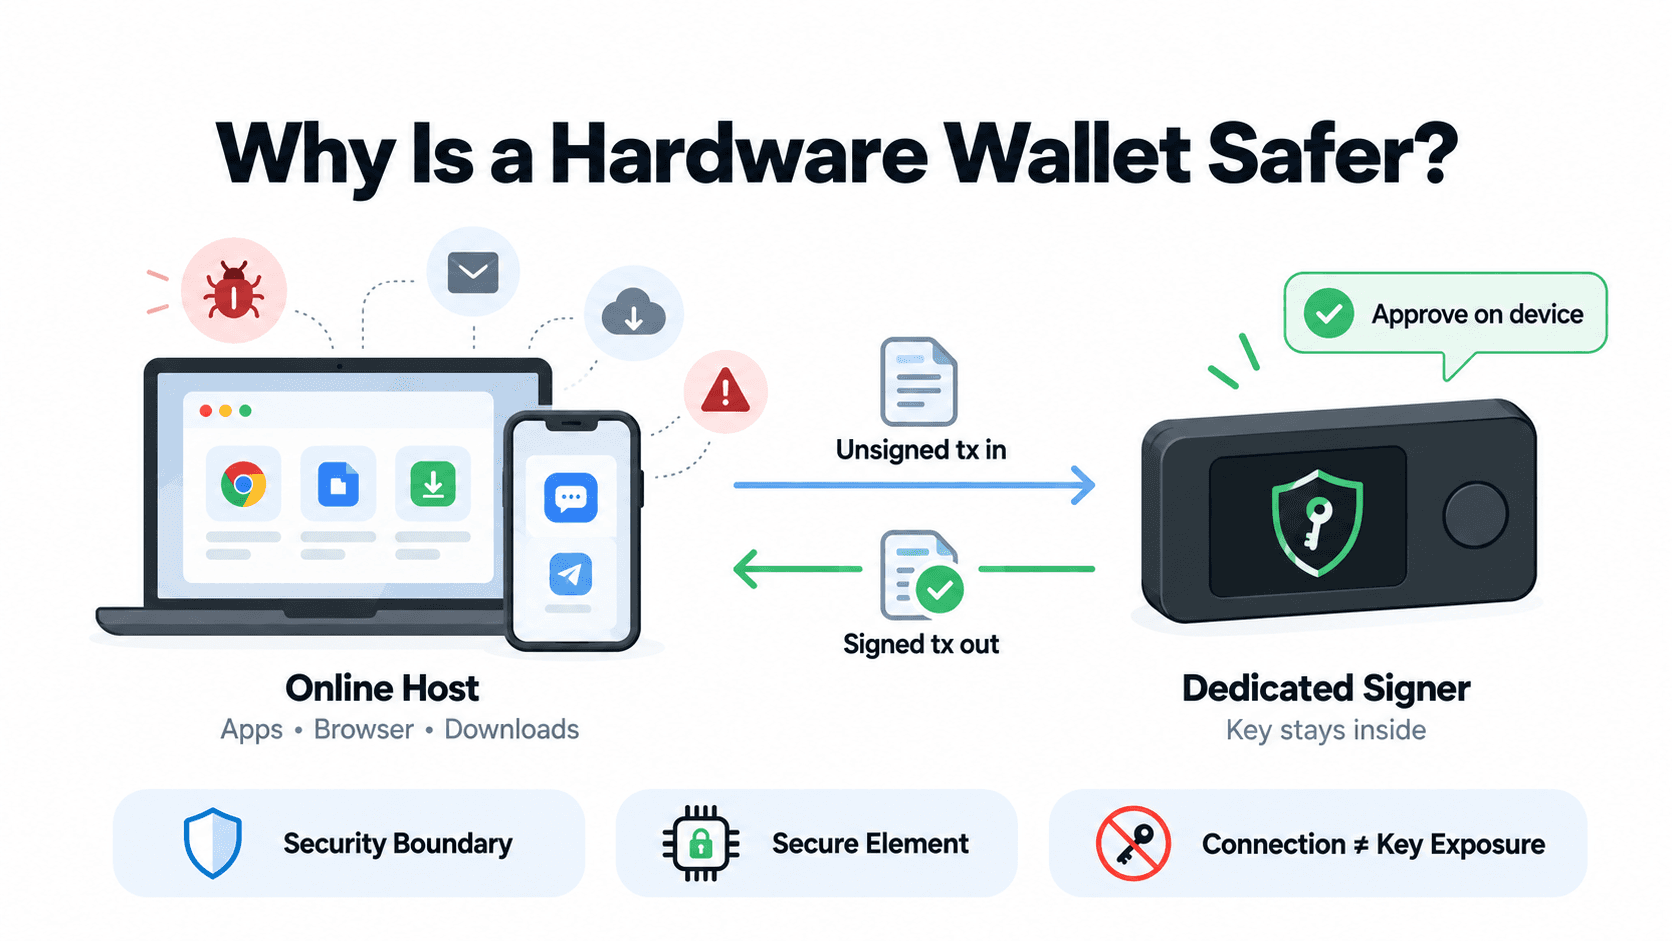 Why Hardware Wallets Create a Stronger Security Boundary
The Security Boundary Between the Hardware Wallet and the Host Device
With a conventional software wallet, the signing environment lives on the same general-purpose device used for everyday computing.
A hardware wallet changes that architecture. The laptop or phone can handle the messy online work while the key stays inside a dedicated signer.
That does not mean the host becomes harmless. Malware could still replace a recipient address, manipulate the transaction being prepared or lure the user into approving something dangerous. The hardware wallet's advantage is that compromise of the host does not automatically give malware direct access to the signing secret.
For readers comparing the broader security models across wallet types, our guide to the best crypto wallets covers hardware, software and other self-custody approaches.
What Secure Elements and Dedicated Hardware Do
A Secure Element is a specialized chip designed to protect sensitive information and resist certain forms of software and physical attack.
Hardware-wallet manufacturers use these chips in different ways. One design may store critical secrets inside the Secure Element. Another may use it to enforce PIN attempts, contribute secure randomness, authenticate the device or protect material used alongside secrets stored elsewhere.
Trezor's current Safe devices provide a good example of why implementation details matter. Its Safe 3 and Safe 5 use an OPTIGA Trust M Secure Element, while the Safe 7 combines multiple security chips with a hardened microcontroller.
You will also see certifications such as Common Criteria EAL6+ in hardware-wallet specifications. Read these carefully. An EAL certification can apply to an evaluated chip or component. It should not be translated into a simplistic "this entire wallet has a security score of six out of seven."
Architecture, firmware, recovery design, transaction verification and user behavior all sit outside a single chip-rating headline.
Does Connecting a Hardware Wallet Make It a Hot Wallet?
Connecting a hardware wallet to a phone or computer does not automatically expose its private keys.
The more useful distinction is whether secret signing material becomes accessible to the online host.
USB, Bluetooth, NFC and QR workflows all transfer information between systems. Communication itself is not equivalent to secret-key exposure.
This also explains why an air gap cannot be treated as automatic proof that one wallet is safer in every respect. A QR-based wallet removes direct electronic connectivity, but the overall security model still includes firmware, transaction parsing, backup design, physical security and what the user actually approves.
What Can a Hardware Wallet Protect You From, and What Can It Not Protect You From?
Hardware wallets are strong at isolating signing keys. Their protection becomes much weaker when the failure occurs outside that boundary.
A useful threat model separates key theft from deceptive authorization, recovery failure and user error.
| Threat | Can a Hardware Wallet Help? | Why |
|---|---|---|
| Malware trying to read the private key from a host computer | Yes, strongly | Signing secrets remain isolated from the ordinary host environment |
| Compromised exchange or custodian | Yes, through self-custody | Assets controlled by your keys are not dependent on that custodian |
| Address manipulation | Yes, if details are verified on-device | The trusted display can expose a mismatch before signing |
| Some physical extraction attacks | Potentially | Protection depends on the device architecture |
| Recovery phrase theft | No | The phrase can recreate signing authority elsewhere |
| Phishing | Only partially | A user can still reveal recovery information or approve a harmful request |
| Wrong recipient | No, if you approve it | A valid signature can authorize an irreversible mistake |
| Malicious smart-contract interaction | No, if approved | Secure key storage does not make the requested action safe |
| Forgotten passphrase | No | Correct recovery information may still be unusable without it |
| Bad backup practices | No | Hardware cannot recreate secret material that has become unrecoverable |
Threats Hardware Wallets Are Designed to Reduce
The clearest benefit is resistance to private-key theft from an infected host. Malware running on a laptop may be able to interfere with the transaction workflow, but a properly designed hardware wallet gives it far less direct access to the key itself.
Self-custody also removes one category of counterparty risk. Funds controlled by your own keys do not disappear simply because the exchange account through which you originally bought them becomes unavailable.
A trusted display can also reduce certain manipulation attacks. If malware replaces the destination address shown on the laptop but the hardware wallet independently shows the actual address being signed, the discrepancy can be caught before authorization.
Hardware architecture may also make physical extraction harder, although resistance varies by device and attack method.
Threats a Hardware Wallet Cannot Automatically Stop
Recovery phrase theft bypasses most of the device's protections. An attacker with valid recovery information can generally recreate the wallet elsewhere and sign transactions without touching the original hardware.
Phishing works for the same reason. Fake support staff, malicious websites and fraudulent apps often attack the owner rather than the Secure Element.
The hardware wallet also cannot rescue a user who deliberately enters a recovery phrase into a malicious website, confirms the wrong recipient, forgets a required passphrase or maintains an unusable backup.
Smart-contract interactions add another category. If the device receives a malicious request and the user approves it, the hardware can perform its cryptographic job perfectly while the resulting transaction still causes a loss.
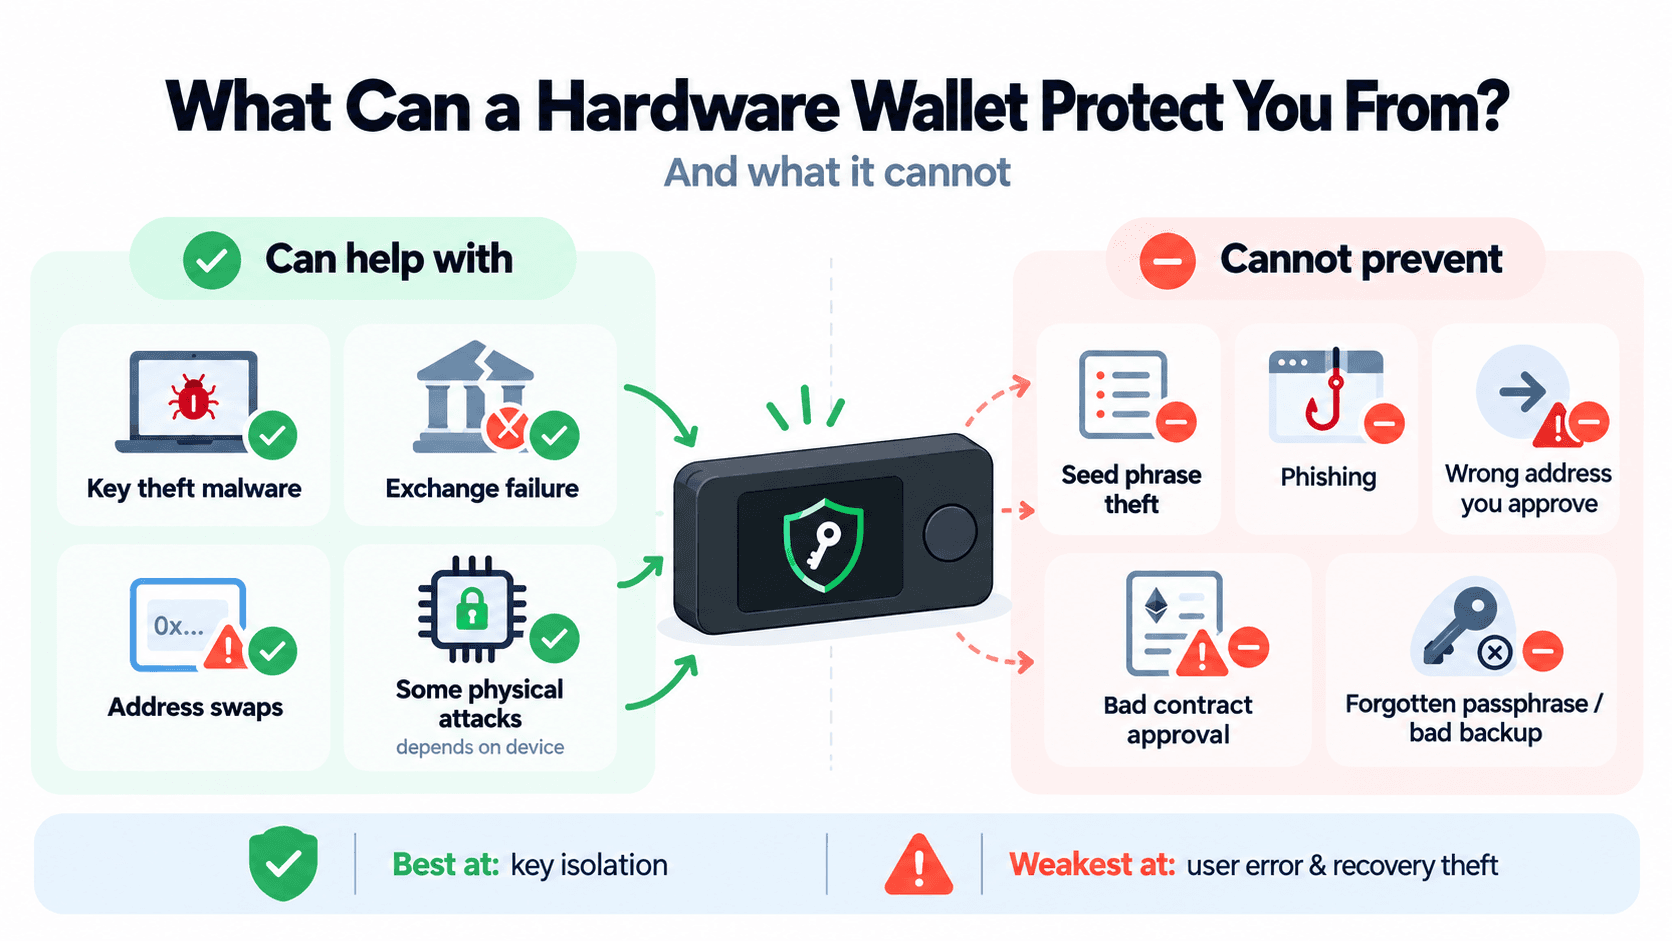 Where Hardware Wallet Protection Ends and User Risk Begins
Why Signing a Bad Transaction Can Still Lose Your Crypto
There is a crucial difference between unauthorized signing and authorized signing of something malicious.
Unauthorized signing means an attacker somehow creates a valid transaction signature without your approval or signing authority.
A malicious authorized transaction follows a different path. The wallet asks for approval. You approve it. The device securely creates the signature. The blockchain sees a valid instruction.
Nothing in basic private-key isolation tells the blockchain whether you understood the transaction.
A token approval is a common example. A user may knowingly sign an on-chain permission while misunderstanding what that permission allows. The private key remains secret throughout the process, yet the resulting authorization can still expose assets.
This is why hardware-wallet security has increasingly shifted toward the quality of transaction verification, not only the secrecy of the key.
What Are Blind Signing and Clear Signing?
Blind signing occurs when a user approves transaction data they cannot meaningfully interpret. Clear signing aims to translate supported transaction data into information a person can inspect before approval.
Why Smart-Contract Transactions Are Harder to Verify
A straightforward token transfer often gives a wallet something intuitive to display: asset, amount and destination.
A smart-contract transaction can be far denser. A DApp may ask the wallet to sign encoded calldata containing function calls, contract addresses, token permissions and other parameters.
Humans are poorly equipped to validate a hexadecimal blob. If the hardware wallet cannot decode that request into meaningful information, the user may be reduced to confirming that "some data" is being signed.
That is blind signing.
The risk is obvious once the transaction model is understood. The device can protect the private key perfectly while the user has very little information about what the signature will authorize.
How Clear Signing Improves Transaction Verification
Clear signing adds a human-readable interpretation layer.
Instead of displaying opaque transaction data, a compatible wallet can show information such as the intended action, token, amount, destination or approval being requested.
Ledger's current clear-signing implementation, for example, displays decoded transaction information on the signer's secure screen, while its developer tooling can resolve supported contract interactions into human-readable fields. Unsupported interactions may still fall back to blind signing.
The broader ecosystem is also working on standardized transaction descriptions. ERC-7730 defines a JSON format for supplying the contextual information needed to present supported EVM contract calls and typed messages in human-readable form.
Clear Signing Does Not Remove the Need to Pay Attention
Clear signing improves visibility. It does not decide whether a financial action is sensible.
A perfectly decoded approval can still be a bad approval. The recipient can still be wrong. The contract itself may be malicious. The DApp may be compromised. An unusual transaction may also lack the metadata required for a clean interpretation.
This leaves the user with the final security decision.
- Blind signing: Approving transaction data the user cannot fully interpret.
- Clear signing: Presenting supported transaction details in a human-readable form before approval.
The progress is meaningful because it tackles a weak point that cold-storage discussions used to gloss over. Keeping the key secret solves one problem. Understanding what the key is being asked to authorize solves another.
How Does Hardware Wallet Recovery Work?
Hardware-wallet recovery works because access depends on recoverable cryptographic secrets rather than the continued survival of one physical device.
A broken screen or dead circuit board is a hardware problem. Losing every valid route to the underlying signing secrets is a custody problem.
What Happens If the Hardware Wallet Is Lost, Broken or Stolen?
If a hardware wallet is destroyed, the blockchain does not know or care.
The assets remain recorded exactly where they were. A compatible replacement can regenerate the relevant wallet if the user still possesses the required recovery information.
Trezor, for example, allows a wallet backup to restore accounts, addresses and private keys after a device is lost, damaged or wiped.
This creates two very different failure scenarios:
- Lost device + valid recovery = usually recoverable access
- Lost device + unrecoverable secrets = potentially permanent loss of access
The physical device is replaceable. The cryptographic authority behind it may not be.
Can You Restore a Wallet on a Different Hardware Wallet?
Yes, widely adopted standards make cross-wallet recovery possible in many cases.
BIP-39 mnemonics, for example, can generate the same underlying seed in compatible implementations. The wallet then needs to use the correct key-derivation rules to find the expected accounts.
Derivation paths matter because wallets can organize accounts differently. BIP-44 provides one common hierarchy built on BIP-32, but networks and wallet software may support additional standards or custom paths.
Coin support also has to be taken into account. A second device may successfully reconstruct the underlying keys while its companion software does not automatically discover every account or support every chain used on the original wallet.
Standard compatibility therefore makes brand-to-brand recovery practical in many cases, but it does not make every feature, derivation path or recovery format universally interchangeable.
What Is a Hardware-Wallet Passphrase?
A passphrase adds another input to the recovery process and derives a different wallet from the same underlying backup.
Under the BIP-39 design, the mnemonic is combined with a passphrase to derive the seed. Every passphrase produces valid derived secret material, which is why there is no universal "wrong password" message that can tell you what you originally used.
In practice, that produces a counterintuitive behavior.
Enter one passphrase and you see one wallet. Enter another valid string and you derive another wallet with different addresses. If that second wallet has never been funded, it looks empty.
A passphrase can add a valuable security layer, but it creates another secret that must survive recovery. Forgetting it can be as consequential as losing the seed.
How Newer Backup Models Differ
Recovery no longer means one universal 12 or 24-word arrangement.
Three broad models now coexist:
- Standard recovery phrases: A mnemonic represents the secret material needed to recreate the deterministic wallet.
- Multi-share recovery: A secret is divided among several shares, with a defined threshold required for reconstruction.
- Alternative or seedless recovery: Wallets can use card-based systems, MPC, passkeys or other architectures that change how signing authority is backed up and restored.
SLIP-39 is one example of the multi-share approach. The SLIP-39 specification uses Shamir's Secret Sharing to divide a master secret into mnemonic shares and allows a minimum threshold of those shares to reconstruct it. It differs materially from a conventional BIP-39 mnemonic.
The backup format changes the recovery workflow. It does not remove the underlying requirement: the owner still needs a reliable way to regain signing authority after device failure.
How to Use a Hardware Wallet Safely
A secure hardware-wallet workflow is straightforward: initialize → back up → verify address → fund → review → sign → maintain.
Most serious mistakes happen when one of those stages is rushed.
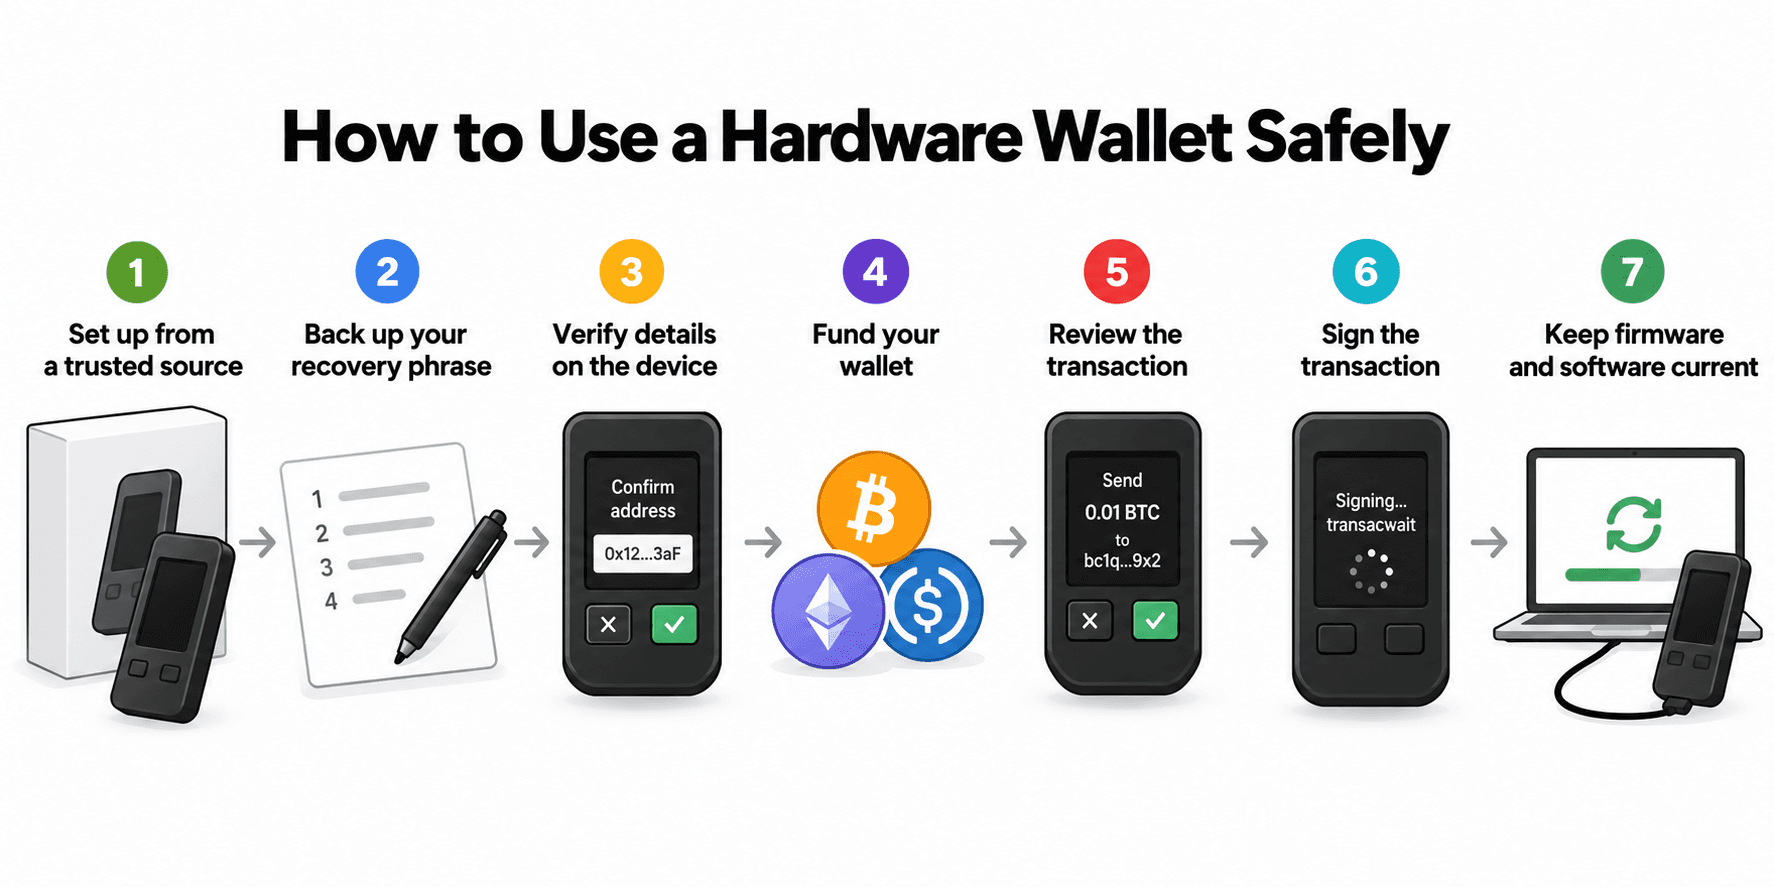 A Safer Workflow for Setting Up Hardware Wallets
Set Up the Wallet From a Trusted Source
Start with a device obtained through a channel you trust. If the manufacturer provides an authenticity check, use it during setup.
Modern devices may use cryptographic device-authentication systems rather than asking the user to judge security from packaging alone.
Install wallet software from the manufacturer's legitimate source, initialize the device and allow the wallet to generate fresh recovery information through its intended setup process.
A pre-written recovery phrase included in the box is a red flag. Someone who already knows those words can potentially reconstruct the wallet.
Tamper stickers can provide information, but they should not become the entire security test. Device authentication, firmware verification and proper initialization are stronger signals.
Back Up the Recovery Information Before Depositing Significant Funds
Record the required backup offline and follow the wallet's recovery instructions precisely.
If the device offers a backup-check function, use it before relying on the wallet for a meaningful balance. A recovery backup that has never been tested is still an assumption.
Do not enter a seed phrase into a random website, browser form, unsolicited support chat or ordinary application. A hardware wallet cannot protect a recovery secret after the user voluntarily gives it to an attacker.
A small recovery test can also help reveal mistakes while the financial consequences are still limited. The objective is simple: prove that the backup recreates the expected wallet before trusting it with funds you cannot afford to lose.
Verify Receiving and Sending Details on the Hardware Wallet
For incoming funds, verify the receiving address on the hardware device before sharing or using it.
For outgoing funds, inspect the recipient, amount and other available information on the hardware display before signing.
A test transaction is often sensible before moving a substantial balance to a new address. It costs an additional network fee, but it can catch address, network or workflow mistakes before the full amount is exposed.
Keep Firmware and Wallet Software Current
Firmware updates can patch vulnerabilities, add network support and improve how transactions are interpreted.
Only install firmware through the manufacturer's legitimate workflow. Confirm that your recovery setup is usable before performing major maintenance on a device holding meaningful funds.
Updating firmware is also conceptually separate from moving crypto. Your blockchain assets do not travel into the firmware file or migrate around the internet during a normal update.
The device software changes. The blockchain continues recording the assets at the same addresses unless a transaction moves them.
Using Hardware Wallets With MetaMask, Rabby and Other Wallet Apps
A software wallet interface can manage a hardware-backed account without becoming the holder of that account's private key.
This is common in DeFi and Web3. MetaMask can connect to multiple hardware wallets through direct connections or air-gapped workflows. Its current hardware-wallet support includes Ledger, Trezor and several QR-based devices, with integrations differing between Extension and Mobile.
The useful separation is between the interface and the signer.
MetaMask or another wallet app can prepare transactions, show balances and connect to DApps. The hardware wallet retains the signing role and must approve outgoing requests.
A MetaMask account generated directly inside the software has a different security model from a hardware-backed account merely displayed through the same interface.
The same basic model can apply to other wallet interfaces, including Rabby: the software can provide the Web3 interface while external hardware retains signing authority.
That still leaves DApp risk. Connecting a hardware wallet to a DApp does not make the protocol, contract or requested approval safe. Every signature still deserves review.
Are Hardware Wallets Worth Using?
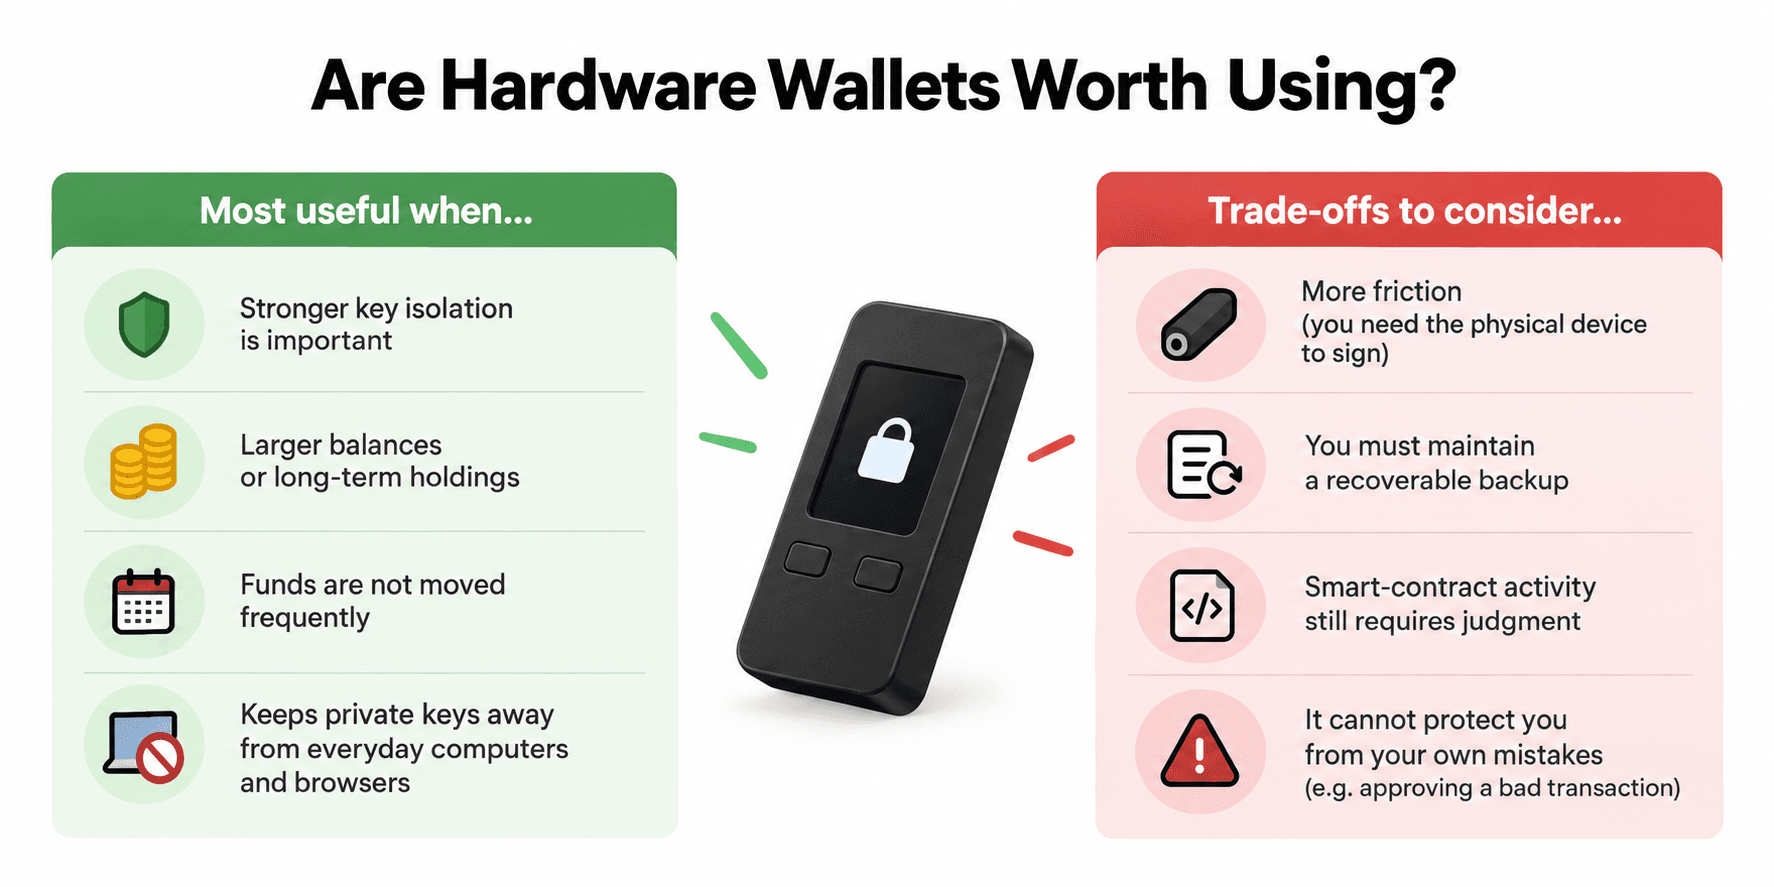
Hardware wallets make the most sense when stronger key isolation is worth a little extra friction.
 When Hardware Wallets Make Sense for Long-Term Self-Custody
They are particularly useful for long-term self-custody, larger balances or funds that do not need constant movement. Keeping the signing secret away from a browser or everyday computer can remove a large class of direct key-theft risk.
The trade-off is convenience. You need the physical signer when authorizing transactions, you need to maintain a recoverable backup, and smart-contract activity still requires judgment.
There is also no universal dollar amount at which someone suddenly "needs" a hardware wallet. The more useful question is how damaging a loss would be and whether an internet-connected signing environment is an acceptable risk for that balance.
Different devices optimize for different priorities. Some focus on large trusted displays, others on Secure Elements, open-source components, QR-based air gaps, mobile NFC workflows, multichain support or alternative recovery models.
That is where comparison pages become more useful than a generic category explanation:
- Use our best hardware wallets guide to compare the current market across security, recovery, asset support and workflow.
- If price is the constraint, our cheap hardware wallets guide covers models under $100 and the compromises that come with budget designs.
- Our hardware wallet vs software wallet comparison is the cleaner starting point if the main question is whether dedicated hardware is necessary at all.
- For deeper attack analysis, read our guide to hardware-wallet security threats, including phishing, malicious approvals, supply-chain risks and physical attacks.
For a tiny spending balance used every day, a reputable software wallet may be perfectly practical. For assets intended to remain untouched for months or years, stronger key isolation becomes much easier to justify.
The physical device is still only one layer. Recovery handling and signing behavior can undo excellent hardware security remarkably quickly.
How Do Hardware Wallets Work? Closing Thoughts
A hardware wallet is a dedicated transaction signer.
The blockchain records the assets. Wallet software prepares transactions, monitors accounts and broadcasts signed requests. The hardware wallet protects the secret signing material and authorizes actions through cryptographic signatures.
That architecture explains both its strength and its limits. Hardware can isolate a private key from an infected computer, yet the user still controls what that key is asked to authorize.
Modern hardware-wallet security is increasingly addressing both sides of that equation: protect the key and make the signature understandable. Trusted displays, richer transaction decoding and clear-signing systems are pushing wallets toward a model where users can inspect more of the actual intent before committing an irreversible blockchain action.
The device secures signing authority. The recovery system keeps that authority recoverable. The screen helps the owner decide when to use it. Understanding those three jobs is far more useful than thinking of a hardware wallet as a USB stick full of cryptocurrency.